Friday, March 30, 2007

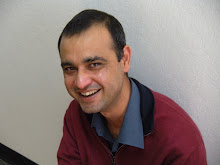
Reflection on Jeff Williams


This week on reflection need no introduction. Jeff Williams, is one of the major contributors in webappsec community. He has written many whitepapers, spoken at many conferences including Secure Software Summit, OWASP conferences, ISSA InfoSec Conference, NSA High Confidence Software and Systems Conference (HCSS), JavaOne, National Computer Security Conference (NCSC), etc, written many tools available at OWASP and also chairs OWASP foundation. Jeff Williams has done a lot of work in promoting awareness of web application security.

On his reflection, Jeff shares with us how he got into web application security and his journey with OWASP and a little bit about his personal life and interests. In his own words

“I set out to be a user interface guy, but I got into security accidentally. I was working at TRW in 1992 on the user interface for a big Navy system that just happened to be highly secure – targeting B2 in the Orange Book. I took on an R&D project to port the user interface to the new compartmented mode workstation (what became Trusted Solaris) and I found that I really liked the challenge of securing such a complex system.

Then Java 1.0 came along and I got NIST and NRL funding to do security research. At the time, we thought the Java sandbox was a good idea, but that there were attacks that might bypass it. So I wrote a special classloader that modified the bytecode to wrap security relevant method calls with a reference monitor. After that I spent several years developing a Java-based multilevel secure network guard on Trusted Solaris. That guard handled HTTP, FTP, TDS, and a number of other protocols – sort of a very early application firewall. But unlike the modern WAFs, we took a whitelist approach where you would define exactly the data formats and rules for allowing messages.

In the mid-90’s, I chaired the group that authored the SSE-CMM, which is now ISO 21827. As it turns out, the processes involved in systems security engineering are quite similar to those necessary for secure software development. I’m very glad to see that the idea of assurance arguments from my work is starting to be used in the application security world.

Then in 1998, while I was the technical director of the Global Security Practice at Exodus Communications, a Fortune 10 company approached us and said “We’d like to host our applications with you, but we have this rule – every line of code has to be reviewed before it goes on the Internet.” So I started an application security practice and started providing application assessments, developer training, and help with security requirements and architecture. We built a successful practice securing some of the biggest and most complex web applications in the world.

In April 2002, together with Dave Wichers, Noelle Hardy, and some other great folks, I started Aspect Security to focus exclusively on application security. I just feel so fortunate to get to work with such an amazing group of consultants and customers. I’m having the most fun of my professional career.

I first heard of OWASP in 2001 from Chuck Pfleeger (the author of Security in Computing). The idea of a free and open community for application security was an interesting idea. At the time, getting companies to focus on application security was difficult. In meetings with several government agencies, they acknowledged that it was an issue, but that they were managing to the SANS Top 20. I came home and literally in the shower said to myself, “I wish we had an application security top ten…” So a small team of us at Aspect took the lead in drafting the first OWASP Top Ten.

Later, Aspect donated WebGoat, a hands-on training environment for application security issues that we had developed for our courses. A huge number of organizations, including Google, use WebGoat today to teach their developers about application security. We started to see that participation in OWASP allowed Aspect to demonstrate our skills in a very constructive way, and many of our customers have contacted us after seeing our participation in OWASP.

I was honored to take over the leadership of OWASP in 2003. At that time, we had a number of great contributors, but OWASP itself was just a domain name and a few small projects. So I got us set up as a 501c3 nonprofit organization and put a management structure in place. I want the OWASP Foundation to provide a free, open, supportive community infrastructure for application security projects. We’re making the barriers to entry for contribution so low that security experts will be motivated to make the effort and share their expertise.

One of the key challenges has been to ensure that OWASP is not influenced by commercial interests. When I set up the AppSec conference and local chapter rules, I made sure that vendors are cannot use OWASP to market their products. We’re also starting to ferret out abuse of the OWASP brand by companies that claim their products “address the OWASP Top Ten” or enable “OWASP Compliance.” The local chapters have been growing very quickly and starting to contribute back to the mothership. Our conferences have also been a great experience.

I think the switch to the MediaWiki platform in 2006 was a major step for OWASP. Prior to that, contributing content was a difficult and painful process. Now, anyone can create an account and contribute easily. We have a team set up to review all the contributions and the number of abuses in our first year has been astoundingly low (less than 10 incidents). We’re to the point now where we get dozens of articles and contributions every day. I don’t see how a non-open approach to building an application security body of knowledge can possibly keep up with our productivity.

We’re still a long way from the point where a company can go to OWASP for everything they need in order to build, acquire, and operate secure applications… but we’ve got an incredible process and we’re working very hard to get there.

I have a wonderful wife Jennifer and three kids, Chance (9), Zack (7), and Zoe (1). We live in the woods and spend a lot of time outside with our four Labrador retrievers. I’m very much into sports – I rowed on the crew team at U.Va. and still play basketball three times a week. For a while I was into extreme rollerblading and then I got into mountain bike trials – I broke a lot of equipment, but never had any serious injuries :)"

Based out of Ashton, MD, Jeff is 39 years old and is the CEO of Aspect Security. Below are his contributions to the webappsec community

Articles / Presentations:-

Opening the Black Box: A Source Code Security Analysis Case Study
http://www.aspectsecurity.com/documents/Aspect_Opening_Black_Box.doc

Application Security Initiatives - The Best Defense Is a Good Offense
http://www.aspectsecurity.com/documents/Application_Security_Initiatives.htm

Let's Sue the Idiots -- Security, Software, Contracts, and Lawyers -
White paper, The OWASP Foundation
http://www.aspectsecurity.com/article/sscl.htm

How to Build an HTTP Request Validation Engine for Your J2EE Application -
White paper, The OWASP Foundation
http://www.aspectsecurity.com/article/bld_HTTP_req_val_engine.htm

Access Control (aka Authorization) in Your J2EE Application -
White paper, The OWASP Foundation
http://www.aspectsecurity.com/article/access_control.htm

Trustworthy Java - Are your apps bulletproof? -
White paper, The OWASP Foundation
http://www.aspectsecurity.com/article/trust_java.htm

The Ten Most Critical Web Application Security Vulnerabilities -
White paper, The OWASP Foundation
http://www.aspectsecurity.com/owasp.htm

Security Code Review - the Best Way to Eliminate Vulnerabilities in Software" -
White paper, Aspect Security
http://www.aspectsecurity.com/documents/AspectCodeReviewWhitePaper.pdf

Can a 'Social Protocol' Help Protect Privacy?
http://www.aspectsecurity.com/documents/p3p.pdf

Jini and Mobile Agent Security -
Proceedings of the Workshop on Agent Technologies (AT ‘98)
http://www.aspectsecurity.com/documents/jini.pdf

A Practical Approach to Improving and Communicating Assurance -
Proceedings of the 10th Canadian Information Technology Security Symposium (CITSS)
http://www.aspectsecurity.com/documents/Arguing.pdf

A Practical Approach to Measuring Assurance -
Proceedings of the 1998 Security Applications Conference (ACSAC)
http://www.aspectsecurity.com/documents/Measuring.pdf

System Security Engineering Capability Maturity Model (SSE-CMM) version 2.0 -
Released at the 21st Annual National Information System Security Conference (NISSC)
http://www.aspectsecurity.com/documents/SSECMMv2Final.pdf

Just Sick about Security -
Proceedings of the New Security Paradigms Workshop
http://www.aspectsecurity.com/documents/Sick.pdf

An Enterprise Assurance Framework -
Proceedings of the 5th Workshop on Enabling Technologies
http://www.aspectsecurity.com/documents/WetIce.pdf

Pretty Good Assurance -
Proceedings of the New Security Paradigms Workshop
http://www.aspectsecurity.com/documents/Pretty.pdf

Need for a Framework for Reasoning about Assurance -
Proceedings of the International Workshop on IT Assurance and Trustworthiness (WITAT)
http://www.aspectsecurity.com/documents/Need.pdf

Assurance is an N-Space (Where N is Hopefully Small) -
Proceedings of the International Invitational Workshop on Developmental Assurance
http://www.aspectsecurity.com/documents/Nspace.pdf

A Capability Maturity Model For Security Engineering -
Proceedings of the 6th Annual Canadian Computer Security Symposium
http://www.aspectsecurity.com/documents/CITSS94.doc

Unsafe at Any (CPU) Speed: Why We Keep Making the Same Mistakes -
NSA High Confidence Software and Systems Conference

Web Applications: The “Last Mile” of Internet Security -
White paper, Exodus Communications

A Constructionist Approach to Law and Society -
Law and Society Seminar, Georgetown University Law Center

Interpreting Anticircumvention (DMCA) -
Advanced International Copyright Law, Georgetown University Law Center

P3I – Protection Profile Process Improvement -
Proceedings of the 22nd National Information System Security Conference (NISSC)
Proceedings of the 10th Canadian Information Technology Security Symposium (CITSS)

Windows NT Security -
17th Annual National Computer Security Conference (NCSC)

Windows NT Client Security and Windows NTAS Security -
The Local Area Network Security Conference (LANSEC)

Reusing Existing C3I Systems in a Secure Environment -
Proceedings of the Application of COTS and Reusable Components Conference

A Framework for Reasoning about Assurance -
Published by the National Computer Security Center of the NSA
Proceedings of the 11th Annual Conference on Computer Assurance (COMPASS)

Interconnecting MLS Command Centers -
White paper for the Multilevel Security Initiative at Hanscomb AFB


Tools written:-

OWASP WebGoat
http://www.owasp.org/webgoat
I built the first WebGoat back in 1998 as a controller servlet with a few simple lessons on SQL injection, cross-site scripting, and access control. Since then, it’s grown to have dozens of lessons and has been revamped several times. Many people have contributed to the project and it’s still quite active.

OWASP Stinger
http://www.owasp.org/stinger
Stinger was a simple idea that every part of every HTTP request should be validated with regular expressions. A mechanism for enforcing a positive security model for validation in an application. It uses a Java “filter” to ensure that all requests are validated and even developers can’t avoid it.

OWASP PDF XSS Attack Filter
https://www.owasp.org/index.php/PDF_Attack_Filter_for_Java_EE
This was a one-night project to build a little filter that generates a token to avoid a specific very dangerous flaw in Adobe Reader.


Contributions:-

OWASP Top Ten
http://www.owasp.org/index.php/OWASP_Top_Ten_Project

OWASP Secure Software Contract Annex
http://www.owasp.org/index.php/OWASP_Secure_Software_Contract_Annex

OWASP Testing Guide (Risk Rating Sections)
http://www.owasp.org/index.php/How_to_value_the_real_risk

OWASP Honeycomb Project (Work in progress)
http://www.owasp.org/index.php/Category:OWASP_Honeycomb_Project


Website:-

http://www.aspectsecurity.com

http://www.owasp.org


Memberships:-

OWASP Chair


Companies worked for:-

Aspect Security
Exodus Communications
Arca Systems
TRW
MITRE


Company working for:-

CEO of Aspect Security


Education:-

JD cum laude – Georgetown Law - Cyberlaw and Intellectual Property
MA – George Mason - Human Factors Engineering
BA – University of Virginia - Cognitive Psychology and Computer Science (Specialization in AI)


I am sure we will see a lot more contribution from him going forward. Though he doesn’t have a blog yet but you can find most of his work on OWASP.

Next Week – Chris Shiflett

Last Week – Robert Auger

Friday, March 23, 2007

Reflection on Robert Auger


This week on Reflection we have someone who has contributed to the webappsec community in many different ways. We all know Robert Auger through http://www.cgisecurity.com/. CGI Security is one of the very early website on the topic and has a wealth of information on web application security. Robert is also a Co-Founder of the Web Application Security Consortium and a founder and moderator of the WASC mailing list. He also co-leads the WASC articles project. Recently he has started http://qasec.com/ where he discusses security testing in the PDLC with an emphasis in QA. He is also leading the WASC Threat Classification (TC v2) project which is currently underway.

Here he shares with us how he got started in webappsec. In his own words

My interest in security sparked in the mid 90's after getting infected with the Stoned Empire Monkey Virus. I was very curious how it and other viruses worked, executed, and hid on my machine. Around the same time I was given access to my high school's VAX/VMS network and met up with a few people creating/setting up fake login screens/key loggers on the dumb terminals spread throughout the school. This VMS network was where I learned my first language 'DCL' and helped out on the local school student run bbs. Sometime later I started reading about 'cgi vulnerabilities' such as the infamous 'phf vulnerability' and was amazed that with nothing more than a browser, I could take over a machine. Since then web based attack research has been my primary hobby (others include finding ways to abuse crawlers and parsers, co running The Web Application Security Consortium, and whitehat/blackhat SEO research).

Based out of Silicon Valley, California, Robert is only in his late 20s, and currently works for a large multinational organization where he focuses on anything application security related. I have had the pleasure of meeting him on a few occasions and not only he is a very friendly guy but very passionate about web application security and can speak to you for hours on the topic. He has enormous knowledge in webappsec field and one of the very few people who also possess good knowledge of security in the Software Development Life Cycle.


Below is a list of his contributions to the webappsec community.


Articles:-


The Cross-site Request Forgery FAQ
The Cross-site Scripting FAQ

Identifying Risks in the Development Cycle

Writing Software Security Test Cases: Putting security test cases into your test plan

Feed Injection in Web 2.0: Hacking RSS and Atom Feed Implementations

Preventing Log Evasion in IIS

Fingerprinting Port 80 Attacks: A look into web server, and web application attack signatures.
http://www.cgisecurity.com/papers/fingerprint-port80.shtml

Fingerprinting Port 80 Attacks: A look into web server, and web application attack signatures: Part Two.

Anatomy of the Web Application Worm

Challenges faced by automated web application security assessment tools


Contributions:-

Founder and Moderator of WASC 'The Web Security Mailing List' http://www.webappsec.org/lists/websecurity/

The Web Application Firewall Evaluation Criteria
http://www.webappsec.org/projects/wafec/

WASC's Threat Classification (TC)
http://www.webappsec.org/projects/threat/

Co-lead the WASC articles project http://www.webappsec.org/projects/articles/guidelines.shtml

The Web Application Security Consortium Web Security Glossary
http://www.webappsec.org/projects/glossary/

Distributed Open Proxy Honeypots Project
http://www.webappsec.org/projects/honeypots/

Contributor to the OWASP Application Security Testing Framework Project
http://web.archive.org/web/20030207091615/www.owasp.org/testing/

Cross-site Tracing (XST): - Research Contributor
http://www.cgisecurity.com/whitehat-mirror/WhitePaper_screen.pdf

A core contributor to Snorts web-attacks.rules rule set


Presentations:-

Zero Day Subscriptions: Using RSS and Atom Feeds As Attack Delivery Systems (Power Point) - Blackhat 2006 presentation
http://www.cgisecurity.com/papers/RSS-Security.ppt


Memberships:-

Co founder of The Web Application Security Consortium http://www.webappsec.org


Email:-

robert_@_@_@_@_@_@_webappsec.org


Blog:-

http://www.cgisecurity.com/


Website(s):-

http://www.cgisecurity.com/
http://www.webappsec.org
http://www.qasec.com/


Companies Worked for:-

SPI Dynamics, Other Consulting companies


Robert is a man of ideas and is already working on some very interesting projects. You should definitely keep an eye out on his websites as we will see a lot more contribution from him soon.

Last Week – Billy Hoffman
Next Week – Jeff Williams

Saturday, March 17, 2007

Reflection on Billy Hoffman


This week on Reflection we have a very young guy from the webappsec field. Billy Hoffman is a lead security researcher for SPI dynamics where he works on discovering and automating web application vulnerabilities and improving their crawling technology. He has presented at a lot of conferences including (ToorCon, Black Hat, etc). Billy’s knowledge on Ajax is tremendous and he has written many papers and presented at many conferences on dangers of using Ajax. Based out of Atlanta, Georgia, he is only 26 years old, the youngest webappsec expert I know of (I am sure there may be younger people too but I am yet to meet them) and like every webappsec expert, his ability to think differently has helped him achieve so much in such a short time. Here he shares with us how he got started in webappsec field. In his own words

“I got started in fall of 1996. My older brother had left for college and he was the one who understood computers. One day the computer stopped working and I wanted to play Doom. So I started fiddling with it and fixed it. About this time I also got a graphing calculator for geometry, so I spend my days writing programs for the TI-85 in Basic and z80 assembler, and my nights writing Basic and learning C. Soon afterwards I actually used one of those AOL disks, discovered the Internet, and learned how to create fake accounts and phish people in the New User Lobby. I wasn’t much of a network guy, let a lone a web hacking guy. In college most of my hacking was focused on hardware or other things that popped on my radar like spy software. I met Caleb Sima, the co-founder and CTO of SPI Dynamics at an Atlanta hacker conference, and he told me to come in for an interview. I was amazed by how vulnerable companies were through their websites. I started in QA, where my job was to verify our crawler and audit engines worked properly. Pretty quickly I saw ways we could improve both, I am now the lead researcher focusing on crawlers and automated vulnerability detection. I continue to speak at security conferences much like I did in college. The only differences now are I speak under my real name, I have an expense report, and there are more middle aged men in Dockers and polos and fewer guys in black t-shirts and green hair! I’ve done a good bit of non-web stuff too. Mainly lots of presentations at different conferences (Interz0ne, Phreaknic, The Fifth Hope), some articles for 2600, O’Reilly’s Make Magazine, etc.”

I got a chance to meet with him in the WASC meetup at RSA. He is a very lively character. Let me put it this way, if billy is a part of a conversation, you won’t get bored even if you just stand there and listen. Below is a list of his contribution to the industry.


Books:

Upcoming book from Addison Wesley this summer tentatively titled “Securing Ajax Applications”


Articles:

“Patching the Holes in Ajax Security,” Cover Story, Software Test and Performance Magazine
http://www.stpmag.com/issues/stp-2007-01.pdf

Stealing Search Engine Queries with JavaScript –
http://www.spidynamics.com/spilabs/education/articles/JS-search.html

Detecting, Analyzing, and Exploiting Intranet Applications using JavaScript –
http://www.spidynamics.com/spilabs/education/articles/JS-portscan.html

Application Error Handling: How to Avoid Death by a Thousand Cuts
http://www.spidynamics.com/spilabs/education/articles/application-error.html

Security Brief - Yamanner Web Worm
http://www.spidynamics.com/spilabs/education/articles/Yahoo-AJAXworm.html

Security Brief – MySpace Quicktime Web Worm
http://www.spidynamics.com/spilabs/education/articles/MySpace-QuickTime%20Worm.html

Ajax Security Dangers Whitepaper
http://www.spidynamics.com/assets/documents/AJAXdangers.pdf

Buiding a Magstripe reader, Cover Story, O’Reilly’s Make Magazine, Issue 1
http://makezine.com/01/magstripe/


Presentations/Conferences:

JavaScript Malware for a Grey Goo Tomorrow - Toorcon 8, Security Opus 2006
http://www.shmoocon.org/schedule.html

Ajax (in)security – BlackHat USA 2006, AJAXWorld, InfoSecurity Canada , SPICON, RSA Conference 2007
http://www.spidynamics.com/spilabs/education/presentations/BillyHoffman-Ajax(in)security.pdf

Analysis of Web Application Worms and Viruses – BlackHat USA 2006 and BlackHat Federal 2006
http://www.spidynamics.com/spilabs/education/presentations/billyhoffman-web_appworms_viruses.pdf

Covert Crawling: A Wolf Among Lambs – Shmoocon 2006, LayerOne 2006. Technology for this talk is used by the MITRE honeyclient project.
http://www.spidynamics.com/spilabs/education/presentations/crawling.html

Layer 7 Fun: Extending Web Apps in Interesting Ways – Phreaknic 9
http://www.msblabs.org/talks/index.php#extending-webapps

Phuture of Phishing – Toorcon 7, FBI Cyber Security Summit
http://www.spidynamics.com/spilabs/education/presentations/phishing.html

Proof of Concepts:

Stealing Search Engine queries with JavaScript
http://www.spidynamics.com/spilabs/js-search/index.html

Portscanning and fingerprinting with JavaSript
http://www.spidynamics.com/spilabs/js-port-scan/

TinyDisk – Filesystem mashup that stores and retrieves data in TinyURL
http://www.msblabs.org/tinydisk/index.php


Memberships:

“Well, ain't it a small world, spiritually speaking. Pete and Delmar just been baptized and saved. I guess I'm the only one that remains unaffiliated.” –Oh Brother Where Art Thou


Tools:

StripSnoop - Suite of research tools that captures, modifies, validates, generates, analyzes, and shares data from magstripe cards. This has received a lot of attention, having been Slashdotted twice, appeared on G4TechTV’s The Screen Savers, and at O’Reilly Emerging Technologies Conference Makers Faire.
http://stripesnoop.sourceforge.net/

Phasmatis – Read and Edits captured data from SpectorSoft’s computer monitoring software
http://phasmatis.sourceforge.net/

TinyDisk – Filesystem mashup that stores and retrieves data in TinyURL
http://www.msblabs.org/tinydisk/index.php

NanoURL – Web Application that provides link shortening services exactly like TinyURL
http://www.msblabs.org/nanourl/index.php

LineBreaker – Anti Phishing Web proxy, released at Toorcon 2005
http://www.spidynamics.com/LineBreaker.zip


Company working for:

SPI Dynamics


Blog:


Website:

Most Significant Bit Labs
http://www.msblabs.org/


Companies worked for:

Crawford and Company, and NetEffects


Education:

BS in Computer Science from Georgia Tech, graduated in 2005.


Billy has a very sharp mind and is very passionate about the webappsec field. He has a bright career ahead of him and is definitely amongst the ones to follow.

Last Week : Sheeraj Shah
Next Week : Robert Auger

Friday, March 09, 2007

Reflection on Sheeraj Shah


This week on Reflection we have another big contributor to webappsec field. Sheeraj Shah is a founder of Net Square Solutions where he performs consulting, training and R&D activities. He has done a lot of research on web application and web services security. Sheeraj started with web application security in mid 2000 when he was working on WebLogic application server and discovered some architecture level security issues. He quickly found out similar issues in other products like WebSphere, JRun, Java Web Server etc. and posted a lot of advisories on SecurityFocus. Since then he has performed numerous network security pen testing and application assessments for many significant companies.


Based out of Ahmedabad, India, Sheeraj is 31 years old and has a lot of experience in web application security and has authored a couple of books, published many articles, presented at many conferences (including Blackhat, HackInTheBox, RSA, etc), and posted several vulnerabilities and advisories at securityfocus. Below is a compilation of most of his work including article, whitepapers, books, presentations, etc


Books:-

Hacking Web Services (Thomson 06)

Web Hacking – Attacks & Defense (AWL 03)


Articles:-

Stateful Web Application Firewalls with .NET
http://www.informit.com/articles/article.asp?p=694855&rl=1

Ajax Fingerprinting for Web 2.0 Applications
http://www.net-security.org/article.php?id=976

Detect Your Web Application's Vulnerabilities Early with Ruby
http://www.devx.com/security/Article/33559

Crawling Ajax-driven Web 2.0 Applications
http://www.net-security.org/article.php?id=973

XSRF attack vector with Ajax serialization
http://searchappsecurity.techtarget.com/tip/0,289483,sid92_gci1235537,00.html

Vulnerability Scanning Web 2.0 Client-Side Components
http://www.securityfocus.com/infocus/1881

Web 2.0 defense with Ajax fingerprinting & filtering
http://www.insecuremagazine.com/INSECURE-Mag-9.pdf

Top 10 Ajax Security Holes and Driving Factors
http://www.net-security.org/article.php?id=956

Detecting Web Application Security Vulnerabilities
http://www.oreillynet.com/pub/a/sysadmin/2006/11/02/webapp_security_scans.html

Hacking Web 2.0 Applications with Firefox
http://www.securityfocus.com/infocus/1879

Top 10 Web 2.0 attack vectors
http://www.net-security.org/article.php?id=949

Assessing Web App Security with Mozilla
http://www.onlamp.com/pub/a/security/2005/10/20/web_vulnerabilities.html

Protect your applications without recoding them
http://www.onlamp.com/pub/a/onlamp/2005/06/09/wss_security.html

Web Services - Attacks and Defense
http://www.net-square.com/whitepapers/WebServices_Info_Gathering.pdf

Defending Web Services using Mod Security (Apache) Methodology and Filtering Techniques
http://www.net-square.com/whitepapers/Defending-web-services.pdf

Web Application Footprints and Discovery
http://www.net-square.com/whitepapers/WebApp_Footprints_Disco.pdf

Web application defense at the gates - Leveraging IHttpModule
http://www.net-square.com/whitepapers/WebApp_HTTPMod.pdf

Web Services: Enumeration and Profiling
http://www.net-square.com/whitepapers/WebServices_Profiling.pdf

Domain Footprinting for Web Applications and Web Services
http://www.net-square.com/whitepapers/domain_footprints.pdf

Web Application Footprinting & Assessment with MSN Search Tricks
http://www.net-square.com/whitepapers/MSN_Search_For_WebApp.pdf

Browser Identification for Web Applications
http://www.net-square.com/whitepapers/browser_ident.pdf


Tools:-

wsChess - Toolkit for Web Services Assessments and Defense
http://www.net-square.com/wschess/index.shtml

MSNPawn - Footprinting, Profiling & Assessment with MSN Search
http://www.net-square.com/msnpawn/index.shtml

Ajaxfinger – Ajax fingerprinting script
http://www.net-square.com/ns_freetools.shtml#ajaxfinger


Presentations:-

Advanced Web Hacking - EUSecWest
http://www.slideshare.net/shreeraj/advanced-web-hacking/

Advanced Web Services Hacking - AusCERT
http://www.slideshare.net/shreeraj/advanced-web-services-hacking/

Web Services Security Chess - RSA
http://www.slideshare.net/shreeraj/web-services-security-chess-rsa/

Web Application Kung-Fu, Art of Defense - Bellua/HITB
http://www.slideshare.net/shreeraj/web-application-kungfu-art-of-defense-bellua/

Hacking and Securing .NET Apps - Infosecworld
http://www.slideshare.net/shreeraj/hacking-and-securing-net-apps-infosecworld/

Defending Web Applications: Strategies, methods and practices
http://www.archive.org/details/hitb2003-Shreeraj-Shah


Blog:-

http://shreeraj.blogspot.com


Companies worked for:-

IBM, Chase bank and Foundstone


Education:-

Masters in Computer Science


Company working for:-

Net Square Solutions Pvt. Ltd.


Email:-

shreeraj__at__net-square__dot__com

Sheeraj has come up with interesting ideas before and i am sure he has a lot more to contribute to the webappsec industry. If you dont already follow his blog then I suggest you should definitely keep an eye on it.

Last Week - Ivan Ristic
Next Week - Billy Hoffman

Friday, March 02, 2007

Reflection on Ivan Ristic


If we hear so much about web application firewalls and their role as a first line of defense in protecting our web applications, a large amount of credit has to go to Ivan Ristic. Ivan Ristic is the creator of ModSecurity (an open source web application firewall and intrusion detection/prevention engine). He started playing in the webappsec space sometime around 2002 and working seriously since 2004. Based out of London, UK, he is only 33 years old and works for Breach Security. He is currently in charge of the ModSecurity product line, which includes ModSecurity, sensor appliances based around it and management appliances. Ivan also wrote Apache Security for O'Reilly, a web security guide for administrators, system architects, and programmers. Prior to web application security, he has worked as a developer, system architect and technical director in the software development industry. He shared briefly his journey with ModSecurity for us. In his own words

"I started developing web applications in 1997. At that time no one really thought about web application security. Since the applications I worked on were sensitive, I had to deal with the problem then or shortly there after. Over time it became apparent to me that designing 100% secure web applications is simply not possible. And even pretty good security is difficult to achieve for an average programmer. The only choice then (and it's the same today) was to fix applications. So the real choice was between having IDS (a network level tool) or a proper HTTP-level tool. Using IDS to deal with HTTP-level problems is very difficult. They will not reassemble transactions and are typically very easy to evade. On top of that most can't see into SSL traffic. So I don't really think there was a choice.

I started working on ModSecurity in November 2002. I came up with a beta version pretty quickly. If I recall 1.2 was the first version to be made available to the public. But it wasn't until 1.5 that I felt comfortable enough with the product to tell others they can use it in production. Version 1.5 was out in May 2003. Although 1.4.2 (February 2003) was actually ready for production, version 1.5 had a web site, manual, mailing lists, etc. In other words the whole package needed for a project.

My biggest hurdle was lack of documentation for Apache and (especially) Apache 2 programming. That's where I spent most of my time in the first couple of years. Getting content interception to work in Apache 1.3.x was difficult because there is no API in Apache 1.3.x for that purpose (so my solution is a hack). And it's been very difficult in Apache 2.0.x because there was no documentation and when there was - it was outdated. In terms of code I always worked on the project alone. But the community is not only about code - I've had a lot of help from various people over the years, in one form or another.

The biggest decision I made was about the model. At the time I was thinking of building a separate program or writing an Apache module. I am still happy with my decision (to write an Apache module) because it allowed me to focus on the areas I really cared about. Plus it allowed me to learn a lot about Apache and that lead me to write Apache Security, which was a tremendous project on its own.

I didn't work for a security company up until 2004. In 2004 I started my own business (Thinking Stone) to support ModSecurity. Thinking Stone was subsequently bought by Breach Security in 2006. I am still working for Breach Security today. We are a web application firewall company.As for the future of Web Application Firewall, I cannot see a world without them. Even if web applications magically become secure overnight, a large part of what I think WAFs do is auditing and monitoring. In other words - defence in depth. I don't see that need ever going away."


Ivan spends his time thinking about web intrusion detection, web application security and security patterns. When he is not working, he spends his time cooking, photography, and studying the English language but most of the time he ends up back in the webappsec space. He is probably the first to talk about the concept of "impedance mismatch" between applications and external security layers. Below are various other contributions from him


Books:-

Apache Security (O'Reilly, 2005)
http://www.apachesecurity.net/
http://www.oreilly.com/catalog/apachesc/index.html


Articles:-

Software Documentation with DocBook Quick HOWTO
http://www.oreillynet.com/sysadmin/blog/2005/11/software_documentation_with_do.html

Web Security Appliance with Apache and ModSecurity
http://www.securityfocus.com/infocus/1739

ModSecurity 2.0 with Ivan Ristic
http://www.securityfocus.com/columnists/418

Introducing mod_security
http://www.onlamp.com/pub/a/apache/2003/11/26/mod_security.html

What's New in ModSecurity
http://www.onlamp.com/pub/a/apache/2005/12/01/modsecurity.html

The public life of Apache Security begins
http://www.oreillynet.com/sysadmin/blog/2005/04/the_public_life_of_apache_secu.html

Web Application Firewalls Primer
http://www.net-security.org/dl/insecure/INSECURE-Mag-5.pdf


Contributions:-


Presentations:-

Web Application Firewalls – When are they useful?
http://www.modsecurity.org/documentation/Web_Application_Firewalls_-_When_Are_They_Useful.pdf

Web Intrusion Detection with Mod Security
http://www.thinkingstone.com/talks/Web_Intrusion_Detection_with_ModSecurity.pdf

Mod Security: Embeddable Web Application Firewall
http://www.thinkingstone.com/talks/ModSecurity_Elevator_Pitch.pdf

Threat Modeling for Web Applications Deployment
http://www.thinkingstone.com/talks/Threat_Modelling.pdf

Apache Security Training
http://www.thinkingstone.com/talks/Apache_Security_Training.pdf


Memberships:-


Tools written by him:-

ModSecurity for Apache
ModSecurity Console
Apache Tools


Blog:-

http://www.modsecurity.org/blog/


Website:-

http://www.modsecurity.org/
http://www.apachesecurity.net/
http://www.ivanristic.com/


Companies worked for:-

Thinking Stone (founder)
DNS Europe
Eunet


Education:-

BSc in Computing & IT.


Email:-

ivanr__at__webkreator__dot__com

Last Week : Jeremiah Grossman
Next Week : Sheeraj Shah

Sunday, February 25, 2007

Separating actual urls hidden behind the link can help reduce phishing

Lately i have been getting a lot of phishing emails in my inbox. Over the years yahoo has done a good job in redirecting those to spam folders. Of course every now and then one or two might slip through the cracks but its only until recently when i started getting a lot of phishing emails in my inbox. Emails for washington mutual, paypal, bank of america, etc. It didnt matter if i have an account with them or not. Luckily Over time i have developed a habit of dragging my mouse over the link to see what is the actual url behind the link. Sure enough, it was taking me to some other website instead of what was shown in the link. What surprises me most is that though phishers have been using the same old method of deceiving the users by making them click on fake urls, the industry is still trying to find all the possible means but not separating the actual url from the link.

Here is an example. I received this in my yahoo mail today. If you drag your mouse over the link, you will see the actual url is something else as mentioned in the link. (Be careful if you click on the url)
https://www.paypal.com/row/vst/id=11791677P5757633F

I know its an ongoing battle between the product managers and the security professionals on Where do you draw a line between a feature and the security. Allowing a user to click on a url is the basic feature of a html page. Html emails use the same feature which is exploited by the phishers and with a great success rate. The point i am trying to make here is email providers are spending a lot of money in creating a robust phishing detection mechanism but giving no attention to the urls. How hard it is to match the actual url with the text mentioned in the link. If it doesnt match then based on other criterias it can be marked as phishing email/spam. If they dont want to mark it as phishing emails, the least they can do is display the actual url separately from the link and let the user copy and paste it, if they want to. Its not a huge inconvenience to the user but at the same timeit can help reduce phishing attempts from the malicious people.

If a phishing url could be displayed like this,

https://www.paypal.com/row/vst/id=11791677P5757633F (http://reseller4.ultrawhb.com/~mrbouble/.public/login.html)

then at least the customer is not fooled and if he copies and pastes the wrong url then there is no solution to that.

Friday, February 23, 2007

Reflection on Jeremiah Grossman

Today’s personality is again well known for its contribution to the world of web application security. Jeremiah Grossman is an expert in webappsec and is a CTO and a co-founder of Whitehat Security. He is also a founding member of Web Application Security Consortium. Jeremiah started hacking around 1991-92 but it was only until 2000, he took it as a profession when he was working for yahoo where he performed various web application security related activities. Over the years he has done a lot of web application security R&D and contributed to the community in various ways. He has spoken at numerous conferences, published a lot of articles, shared a lot of research ideas and made various other contributions including but not limited to Internet Security Apache Benchmark Group and Web Application Security Consortium. In his spare time he trains in Brazilian Jiu Jitsu and play australian rules football and his specialty is web application security, web development, Australian rules football and video game hacking.

Jeremiah is based out of San Jose, CA and is only 29 years old and has spoken at numerous conferences all over the world including Black Hat, ISSA, ISACA, NASA, RSA, OWASP, AFITC, Stanford and many other industry events. His research, writings, and discoveries have featured in USA Today, VAR Business, NBC, ABC News (AU), ZDNet, eWeek, BetaNews, etc. Below is a compilation of most of his work, which by no means, covers his entire contribution.


Articles / Books:-

Ten Things You Should Know about Web Application Security
http://www.whitehatsec.com/downloads/WP10Things.pdf

The 80/20 Rule for Web Application Security
http://www.webappsec.org/projects/articles/013105.shtml

Chasing Vulnerabilities for Fun and Profit
http://www.whitehatsec.com/articles/chasing_vulnerabilities.shtml

Myth-Busting AJAX (In)Security
http://www.whitehatsec.com/home/resources/articles/files/myth_busting_ajax_insecurity.html

Myth-Busting Web Application Buffer Overflows
http://www.whitehatsec.com/articles/mythbusting_buffer_overflow.shtml

Pay Now or Pay Later: Obtaining ROI from Web Security
http://www.cunews.com/roundtable/WhiteHat3.pdf

Technology Alone Cannot Defeat Web Application Attacks
http://searchsoftwarequality.techtarget.com/tip/0,289483,sid92_gci1189767,00.html

Insecure Web Sites
http://www.varbusiness.com/showArticle.jhtml?articleID=18825528

Thwarting SQL Web Hacks
http://www.varbusiness.com/showArticle.jhtml?articleID=18841325

Top 5 Myths of Web Application Security
http://www.varbusiness.com/showArticle.jhtml?articleID=22104030

Web Application Security 101
http://www.whitehatsec.com/articles/webappsec101.pdf

What Phishers Know That You Don't
http://www.betanews.com/article/What_Phishers_Know_That_You_Dont/1114784531

Cross-Site Scripting Worms and Viruses
http://www.whitehatsec.com/downloads/WHXSSThreats.pdf

Top 10 Web Hack of 2006
http://www.whitehatsec.com/home/resources/presentations/files/whitehat_top_hacks_06_F.pdf
Most of the recent ones are listed here:
http://jeremiahgrossman.blogspot.com/2006/12/top-10-web-hacks-of-2006.html

Automated Scanner vs. The OWASP Top Ten
http://jeremiahgrossman.blogspot.com/2007/01/automated-scanner-vs-owasp-top-ten.html

He is also co-authoring a book on XSS to be released tentatively on March 1, 2007
Cross Site Scripting Attacks: XSS Exploits and Defense

He also wrote the foreword for two books:-

Preventing Web Attacks with Apache
http://www.amazon.com/Preventing-Attacks-Apache-Ryan-Barnett/dp/

Hacking Exposed Web Applications, Second Edition
http://www.amazon.com/Hacking-Exposed-Web-Applications-Second/dp/


Contributions:-


Presentations:-

Hacking Intranet Websites from the Outside (Session code: HT2-107)
http://news.thomasnet.com/companystory/506356

Hacking Intranet Websites from the outside - "JavaScript malware just got a lot more dangerous"
http://www.blackhat.com/html/bh-usa-06/bh-usa-06-speakers.html#Grossman

Phishing with super bait
http://www.blackhat.com/presentations/bh-usa-05/bh-us-05-grossman.pdf

Challenges of Automated Web Application Scanning
http://www.blackhat.com/presentations/bh-federal-03/bh-fed-03-grossman-up.pdf

Webserver Fingerprinting
http://www.whitehatsec.com/presentations/Black_Hat_Singapore_2002/BlackHat2002-Singapore.zip

The land that application security forgot
http://opensores.thebunker.net/pub/mirrors/blackhat/presentations/bh-europe-01/jeremiah-grossman/bh-europe-01-grossman.ppt

Hacking Intranet Websites from the Outside with JavaScript Malware Dang (CSI NetSec)
https://www.cmpevents.com/CSINS7/a.asp?option=C&V=11&SessID=4896

StillSecure, After all these years, Podcast #28
http://www.stillsecureafteralltheseyears.com/ashimmy/2007/01/episode_28_of_s.html

Cross-Site Tracing (XST)
http://www.cgisecurity.com/whitehat-mirror/WH-WhitePaper_XST_ebook.pdf

Automated Scanners vs. Low-Hanging Fruit
http://jeremiahgrossman.blogspot.com/2007/02/automated-scanners-vs-low-hanging-fruit.html


Speaking engagements:-

Jeremiah Grossman TV interview with ABC News (AU)
http://www.youtube.com/watch?v=HPutgmAzgQA

ISSA NORCAL Systems Security Symposium 2004, Network Security Conference 2004 – Web Application Security Auditing
http://www.issa-sac.org/conferences/2004/presentations.php#

Black Hat 2006 - Hacking Intranet Websites from the Outside "JavaScript malware just got a lot more dangerous"
http://www.blackhat.com/html/bh-japan-06/bh-jp-06-en-speakers.html#Grossman

Black Hat 2005 - Phishing with Super Bait
http://www.blackhat.com/html/bh-usa-05/bh-usa-05-speakers.html#grossman

Black Hat USA 2004 - Panelist
http://www.blackhat.com/html/bh-usa-04/bh-usa-04-speakers.html

AITP Central Valley – Web Application Security http://www.whitehatsec.com/presentations/AITP_CentralValley_062004.pdf

ISSA Sacramento 2004 – Auditing Web Applications
http://www.issa-sac.org/conferences/2004/presentations.php#

Blackhat Seattle 2004
http://www.blackhat.com/presentations/bh-federal-03/bh-fed-03-grossman-up.pdf

BlackHat Windows 2003 – Hacking Web Applications Training Class, Detecting Web Application Attacks Presentation
http://www.blackhat.com/html/win-usa-03/train-bh-win-03-wh.html

Blackhat New Orleans 2002 – Web Application Security and Arsenal http://www.blackhat.com/presentations/win-usa-02/grossman-winsec2002.ppt

Blackhat Europe 2001 – Web Application Security http://www.blackhat.com/presentations/bh-europe-01/jeremiah-grossman/bh-europe-01-grossman.ppt

Air Force Information Technology Conference 2001, Web Application Security
http://www.whitehatsec.com/presentations/AFITC_2001/afitc_2001.ppt

DefCon Las Vegas 2001 – Web Application Security in Theory and Practice
http://www.whitehatsec.com/presentations/Defcon9_2001/defcon9_presentation2001.ppt

Speaker and Panelist for the Web Application Security Forum (Tokyo, Japan) - “WASC Activities and U.S. Web Application Security Trends”
http://www.whitehatsec.com/presentations/WASC_WASF_1.02.pdf

Blackhat Singapore 2002 – Web Server Fingerprinting - "A first look into web server fingerprinting"
http://www.blackhat.com/presentations/bh-asia-02/bh-asia-02-grossman.pdf

Podcast with ITRadio (Risky Business #1)
http://www.itradio.com.au/?p=6

Credit Union Information Security Conference Panelist 2004 http://www.cunews.com/infosec.htm

Washington Software Alliance 2003 / ISSA Pugeot Sound 2003 / Blackhat Federal 2003 / SuperCIO 2003 / NASA AMES 2003 – Challenges of Automated Web Application Scanning
http://www.whitehatsec.com/presentations/NASA_AMES_2003_v1.0.ppt

ISSA San Diego – Auditing Web Applications
http://www.whitehatsec.com/presentations/Auditing-Web%20Applications.pdf

ToorCon San Diego 2001 (Couldn’t find the url)


Proof of concepts:-

Intranet Hacking
http://jeremiahgrossman.blogspot.com/2006/09/video-hacking-intranet-websites-from.html

Browser Port Scanning without JavaScript
http://jeremiahgrossman.blogspot.com/2006/11/browser-port-scanning-without.html

Bypassing Mozilla Port Blocking
http://jeremiahgrossman.blogspot.com/2006/11/bypassing-mozilla-port-blocking.html

I know if you're logged-in, anywhere
http://jeremiahgrossman.blogspot.com/2006/12/i-know-if-youre-logged-in-anywhere.html

I know where you’ve been
http://jeremiahgrossman.blogspot.com/2006/08/i-know-where-youve-been.html

Goodbye Applet, Hello NAT'ed IP Address
http://jeremiahgrossman.blogspot.com/2007/01/goodbye-applet-hello-nated-ip-address.html

JavaScript Array Overwriting - Advanced Web Attack Techniques using GMail
http://jeremiahgrossman.blogspot.com/2006/01/advanced-web-attack-techniques-using.html


Tools written by him:-

WhiteHat Webserver Fingerprinter (no longer available)http://www.whitehatsec.com/presentations/Black_Hat_Singapore_2002/wh_webserver_fingerprinter.tgz

Scoring Tool CIS for the Apache Benchmark
http://www.cisecurity.org/bench_apache.html

WhiteHat Arsenal (no longer available)


Memberships:-

WASC Co-Founder


Blog:-

http://jeremiahgrossman.blogspot.com


Website:-

www.whitehatsec.com


Companies worked for:-

Amgen, Yahoo, WhiteHat


Email:-

jeremiah__at__whitehatsec__dot__com


He is a man of ideas and thinks differently from others. His blog is amongst the most followed blogs on information security. A must follow figure in web application security to stay current with emerging threats and news.

Last Week – RSnake
Next Week – Ivan Ristic

Tuesday, February 20, 2007

Compliance - is it worth the money?

While surfing through the net i found a posting on compliance
http://bestsecurity.blogspot.com/2007/02/compliance-audit-is-not-substantive.html

Though it was more of a ranting on the compliance but it certainly made me think my experience on PCI compliance.

I do agree that compliance has a place in the industry. In my experience, had it not been for compliance, many companies have not paid attention towards web application security at all. Unfortunately, many of the product managers or project managers (in big enterprises) still do not understand the issue of web application security (or should i say don't want to understand) and hence we see a lot of vulnerable applications out there. As for small and medium businesses, the sheer cost of securing web applications in itself makes them not go for the solutions. Compliance in a way is forcing them to do something about it. However, the problem starts from the governing agencies enforcing compliance. Take PCI compliance for example. It all started as a good idea to enforce companies to secure customer information but then they lost focus along the way. It is OK as long as you are making sure if the network and the applications aren't vulnerable but if you want to enforce a company to have source code audit by an independent third party, that is where it gets ridiculous.
What about companies who doesnt want to reveal their source code? what if it is proprietary software? Can I trust the company who is doing my source code audit, more importantly can I trust the person who is doing my source code audit? We have seen cases of hackersafe signing websites that they are safe from hackers and we have seen cases of bank's employees (who are the guardians of the customer information) selling the very customer information to the outside agencies. Who can I trust? Not to say what is the guarantee that the person doing the source code audit has enough knowledge of the language and more importantly where are the secure coding guidelines for us to follow?
The sheer cost of doing web application security compliance including black box testing, white box testing, source code analysis, web application firewall, etc, etc will run into hundreds of thousands of dollars (as we saw in RSA Conference) and not to mention the amount you have to pay for the auditors.

The other ugly side of compliance is auditing companies. For PCI compliance, there have been too many companies doing auditing for price ranging from $1000 to $13000. This confused me in the beginning and I started to ask questions about what is the value addition for that extra money and after doing a lot of research, I found out it's not about the value addition for the extra money, it's about saving your neck. When you can buy a compliance certificate for $1000 then why do you want to pay $13000. Of course, if you really are concerned about your security and want to do things the right way, then the price definitely will not be $1000.

I am sorry to say but compliance has become just another way for auditing companies to make money and the real message has gotten lost.

Thursday, February 15, 2007

Reflection on RSnake


If you have heard of XSS cheat sheet or http://ha.ckers.org/ then you already know him. His name is Robert Hansen or more popularly known as RSnake. If there is any mention of XSS, there is a big chance RSnake’s name or its cheat sheet is mentioned along with it. His contribution in the web application security awareness is legendary. On two of his many web sites (http://ha.ckers.org/ and http://sla.ckers.org/ ) you will find a wealth of information on various aspects of webappsec. His XSS cheat sheet is arguably the most referenced link in the webappsec space with 27000 hits in the month of January ’07 alone and http://ha.ckers.org/ has around 10,000 unique visitors per day (not counting the RSS feeds) making it probably the most followed blog in webappsec field. He has shared his technical expertise with a lot of industry professionals in their work including but not limited to working with Microsoft engineers to address XSS issue, Cloaking to Stop Scraping, and his discussion with the author of the chilling effect.

Looking at his past, he started hacking when he entered college, which was when the web applications were just getting started. In his words

"I'm a college dropout but was studying Computer Engineering. It was way too boring. They were dealing with the theoretical nuances of computers and outdated technology (Pascal pseudo-code on Macintosh assembler). At the same time that I was going to school, in my part time jobs I was doing in practice what my professors could only barely grasp from a theoretical perspective. This was pre-bubble and my parents and my teachers were telling me to get out there and make my millions. I took angel funding for a project, and everything seemed to be going well, but then the stock market crashed, investment money dried up and I learned a hard lesson. It was the day I closed up shop at my own company that I learned everything I need to know about business.
My first PERL script was a top100 list for webfringe.com (long gone now). I had a lot of people trying to hack it. It was a fun experiment that I finally gave up on due to time issues, but it gave me a lot of insight into how you can spoof traffic. Hackers have some of the most interesting traffic on the Internet. It's a pleasure to host security sites, because I get great visibility into the techniques and tools.”

RSnake is currently based out of California but is planning to move to Texas, US and start his own company SecTheory. In the WASC meetup I got a chance to meet with him, and for a person who is known and respected by the hackers and security professionals alike, he is very down to earth and with a good sense of humor, unlike a typical geek. Below are some of his contributions to the webappsec community. I say some because the information below does not represent all his work. Even he has lost track of some of his work over the years.

Articles / Books

PGP Man in the Middle Attack

AcuTrust Entropy Attacks

Hardening HTAccess, Part One

Hardening HTAccess, Part Two

Hardening HTAccess, Part Three

Accessing Trillian Pro Remotely and Through an Encrypted Tunnel

Death By 1000 Cuts – a Case Study
http://ha.ckers.org/deathby1000cuts/

Is your money safe?
http://ha.ckers.org/old/

Electronic Commerce Insecurity
http://ha.ckers.org/old/10102002.shtml

Internet Mind Games
http://ha.ckers.org/old/07221998.shtml

Apache Information Disclosure Issues or, "How to detect cloaking"
http://www.secureseo.com/blog/2006/04_07_apache_information_disclosure_issues.html

He is also co-authoring a book on XSS to be released tentatively on March 1, 2007
Cross Site Scripting Attacks: XSS Exploits and Defense


Tools written by him:-

Fierce
http://ha.ckers.org/fierce/

MHTML framework
http://ha.ckers.org/weird/mhtml.zip

XSS fuzzer
http://ha.ckers.org/fuzzer/XSSFuzz.zip


Contributions:-

Lots of changes to browser technology over the years. Started a number of security sites, written hundreds of articles, dozens of tools and many sample PoC. He has also presented at Blackhat USA and Networld+Interop on a Security Information Management roundtable (couldn’t find the url)


Blogs:-

Web Application Security Blog
http://ha.ckers.org/

Snake Bytes
http://www.darkreading.com/blog.asp?blog_sectionid=403


Websites:-

He had started many security related sites, but these two are most popular

To discuss any aspect on web application security
http://sla.ckers.org

If you want a break from your work and need a quick laugh
http://www.fthe.net/


Memberships:-

ISSA, CISSP, OWASP, WASC, IASCP. He is also working on something to certify web application security engineers.


Companies worked for:-

He has worked for a major banner advertising company as an Information Specialist and for several start-up companies as Chief Operations Officer and Chief Security Officer. He is now starting his new company SecTheory - doing boutique web application and network security consulting.


Email:-

h__at__ckers.org

We will see a lot more contribution from him as he is working on some very cool stuff and if you want to stay on top of webappsec then make http://ha.ckers.org/ as the first site you visit to. I wish him all the best in his new endeavor.


Last Week – Amit Klein
Next Week – Jeremiah Grossman

Tuesday, February 13, 2007

I dont want a product, I want a solution

RSA Expo is over, and it was good to see a lot of Web application security products being showcased there. The awareness about Web application security is increasing, and a lot of companies are coming out with new products to protect Web applications. Such products include network and Web application firewalls, identity management, auditing tools, Web application security tools and encryption tools. If there's a way your company can be hacked, there was a product to protect it.

read the entire article here

Thursday, February 08, 2007

Reflection on Amit Klein


For those who are in the web application security field need no introduction to his name. He is an expert and by far one of the best in web application security space. He is one of the early starters of the field and has played a major role in the awareness of webappsec. His contribution ranges from not only identifying vulnerabilities and publishing them but also contributing towards standards like OWASP guide, WASC threat classification or web application firewall criteria. And those who are not aware should know he was the one who also contributed towards the solution for UXSS (pdf xss vulnerability). He is also a WASC (Web Application Security Consortium) officer and a board member and co-leads the WASC articles project.

Based out of Israel, he started back in 1997 with Perfecto Technologies (which later became Sanctum), mostly heading security research activities. Sanctum was later acquired by Watchfire in 2004 which is when he left Sanctum / Watchfire. He is currently a CTO of a security company.

Below you will find a list of his articles, contributions, presentations and other details.

Articles:-

A Refreshing Look at Redirection
http://www.securityfocus.com/archive/1/450418

Sending arbitrary HTTP requests with Flash 7/8 (+IE 6.0)
http://www.securityfocus.com/archive/1/443391

Under some conditions, it's possible to steal HTTP credentials using Flash
http://www.securityfocus.com/archive/1/443191

Forging HTTP request headers with Flash
http://www.securityfocus.com/archive/1/441014

IE + some popular forward proxy servers = XSS, defacement (browser cache
poisoning)
http://www.securityfocus.com/archive/1/434931

Path Insecurity
http://www.webappsec.org/lists/websecurity/archive/2006-03/msg00000.html

HTTP Response Smuggling
http://www.securityfocus.com/archive/1/425593

Domain Contamination
http://www.webappsec.org/projects/articles/020606.txt

XST Strikes Back
http://www.securityfocus.com/archive/1/423028

Exploiting the XmlHttpRequest object in IE - Referrer spoofing, and a
lot more...
http://www.securityfocus.com/archive/1/411585

Detecting and Preventing HTTP Response Splitting and HTTP Request
Smuggling Attacks at the TCP Level
http://www.securityfocus.com/archive/1/408135

NTLM HTTP Authentication is Insecure by Design
http://www.securityfocus.com/archive/1/405541

Can HTTP Request Smuggling be blocked by Web Application Firewalls
http://www.webappsec.org/lists/websecurity/archive/2005-06/msg00123.html

DOM Based Cross Site Scripting
http://www.webappsec.org/projects/articles/071105.html

Meanwhile, on the other side of the web server
http://www.itsecurity.com/security.htm?s=3957

HTTP Request Smuggling (with Chaim Linhart, Ronen Heled and Steve Orrin)
http://www.cgisecurity.com/lib/HTTP-Request-Smuggling.pdf

The Insecure Indexing Vulnerability - Attacks Against Local Search Engines
http://www.webappsec.org/projects/articles/022805-clean.html

Detecting and Testing HTTP Response Splitting Using a Browser
http://www.securityfocus.com/archive/107/378523

Blind XPath Injection
http://www.packetstormsecurity.org/papers/bypass/Blind_XPath_Injection_20040518.pdf

Divide and Conquer - HTTP Response Splitting, Web Cache Poisoning
Attacks, and Other Topics
http://www.packetstormsecurity.org/papers/general/whitepaper_httpresponse.pdf

Secure Coding Practices for Microsoft ASP.NET
http://www.cgisecurity.com/lib/WhitePaper_Secure_Coding_Practices_VSdotNET.pdf

XS(T) attack variants which can, in some cases, eliminate the need for TRACE
http://www.securityfocus.com/archive/107/308433

Cross Site Scripting Explained
http://crypto.stanford.edu/cs155/CSS.pdf

Hacking Web Applications Using Cookie Poisoning
http://www.cgisecurity.com/lib/CookiePoisoningByline.pdf

Contributions:-

OWASP guide to building secure web application
http://internap.dl.sourceforge.net/sourceforge/owasp/OWASPGuide2.0.1.pdf

WAFEC
http://www.webappsec.org/projects/wafec/

WASC's Threat Categorization (TC)
http://www.webappsec.org/projects/threat/

Co-lead the WASC articles project
http://www.webappsec.org/projects/articles/guidelines.shtml

Presentations:-

OWASP AppSec Europe Conference 2006 – “HTTP Message Splitting, Smuggling and Other Animals”

CERT 2002 Conference, August 2002 - "WWW Forensics"

FM'99 Congress, September 1999 - "A Perfect Verification: Combining Model Checking with Deductive Analysis to Verify Real-Life Software"

Memberships:-

Amit is WASC officer and board member.

Companies worked for:-

Sanctum, Cyota (RSA security)

Education:-

B. Sc. Mathematics and Physics

Email:-

aksecurity__at__gmail_dot_com

And this just doesn't end here, you will see a lot more coming from him. He is a must follow figure of the webappsec field.

Next Friday – Reflection on RSnake

Wednesday, February 07, 2007

WASC meetup during RSA conference

Today at WASC meetup, quite a lot of crowd turned out and it was fun meeting a lot of players from the application security field. Here are some of the pictures from the meetup. You will see people like Jeremiah Grossman, RSnake, Arian Evans (Whitehat), Billy Hoffman (SPI), Robert Auger (cgisecurity.net), etc


You can view more pictures at Jeremiah's blog